Dither Noise Improves LLM Prevents Compounding Insanity
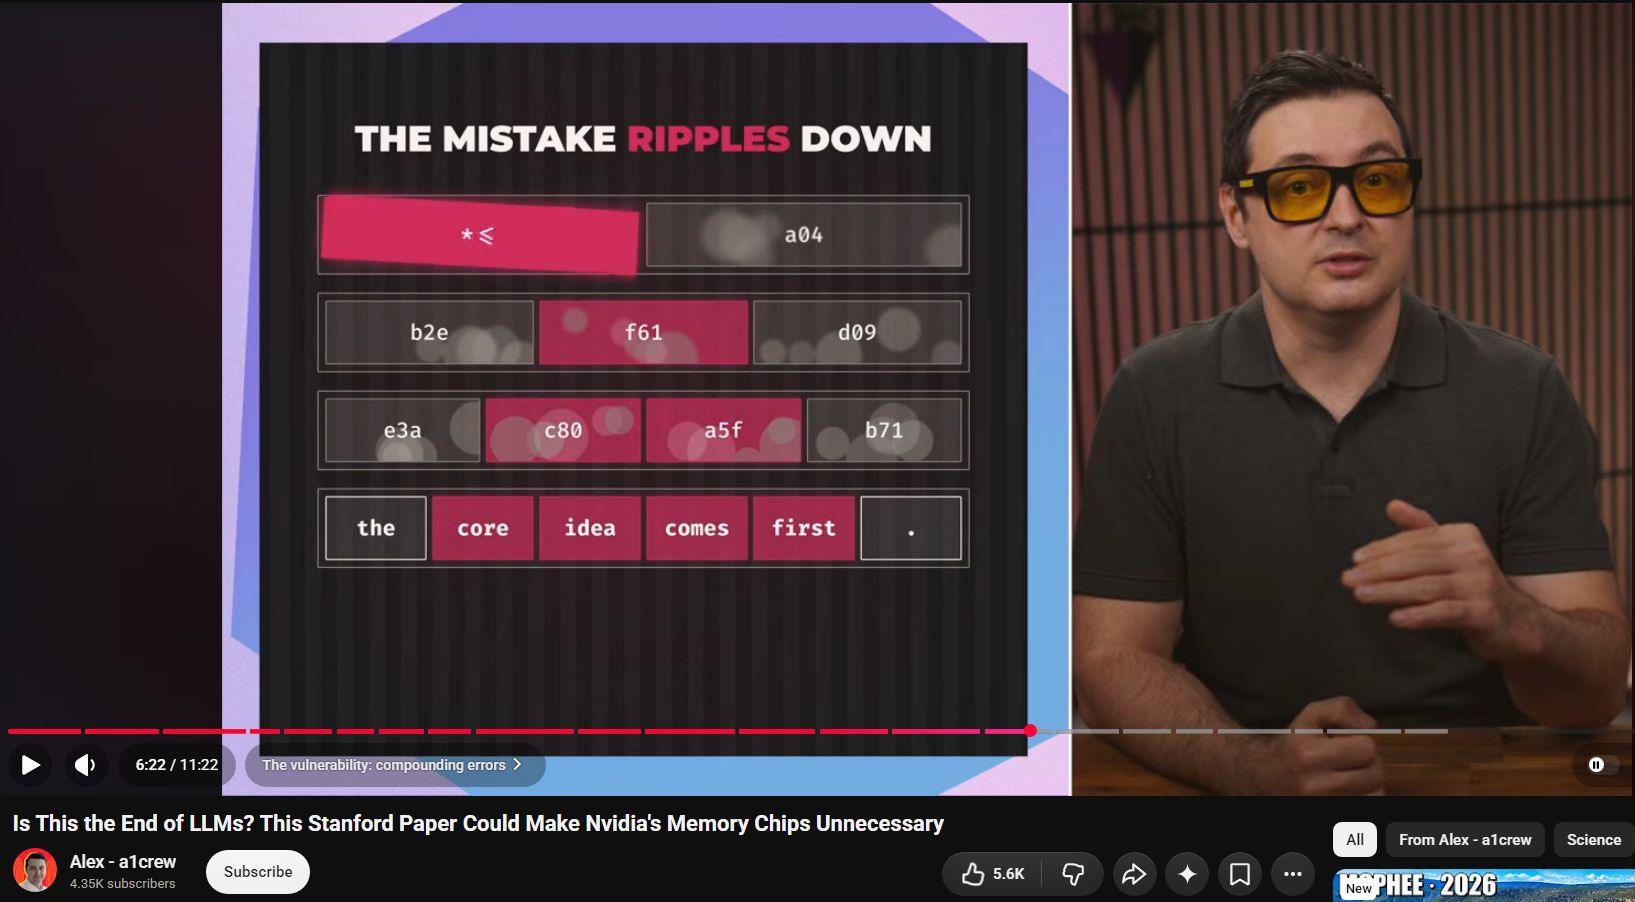
So funny, was thinking of injecting “noise” some months ago to possibly improve LLM — RE digital audio sound improved by injection of noise called “dither”. Stanford paper shows that was actually insightful. The helps prevent ‘death spiral’ (the resource-wasteful reaching of massive yet insane conclusion) due to perturbations on higher / earlier hallucinations. I … Read more
google made Kubernetes K8S, but 99pct of Companies Are Not Google, making K8S = SFTS Silly From The Start
Reminds of X509 ‘full monte’ security, another overblown monster. Kubernetes orchestrates thousands of containers, but maintaining the orchestrator itself costs more: The sought ‘microservice-everything’ counterproductively sucks time and cost via management versus writing business logic — not an engineered solution but instead an awful and expensive liability. The smartest CTOs in 2026 aren’t those hyping … Read more
FireFox is Screwing Itself via Us First – How but not yet Why
We’ve been using a browser session cookie named “cookie” for decades. Preposterously, firefox since ‘some time ago’ (within past year) has been blocking that cookie name as somehow insecure; today it bloomed to emergency head. Absurd inability and/or unwillingness to abide basic published standards ruins time and trust. Firefox has self-downgraded again. Perfect. This is … Read more
American Serhant – “…sell this to people who might hit people; what they do with the bat is not our responsibility.”
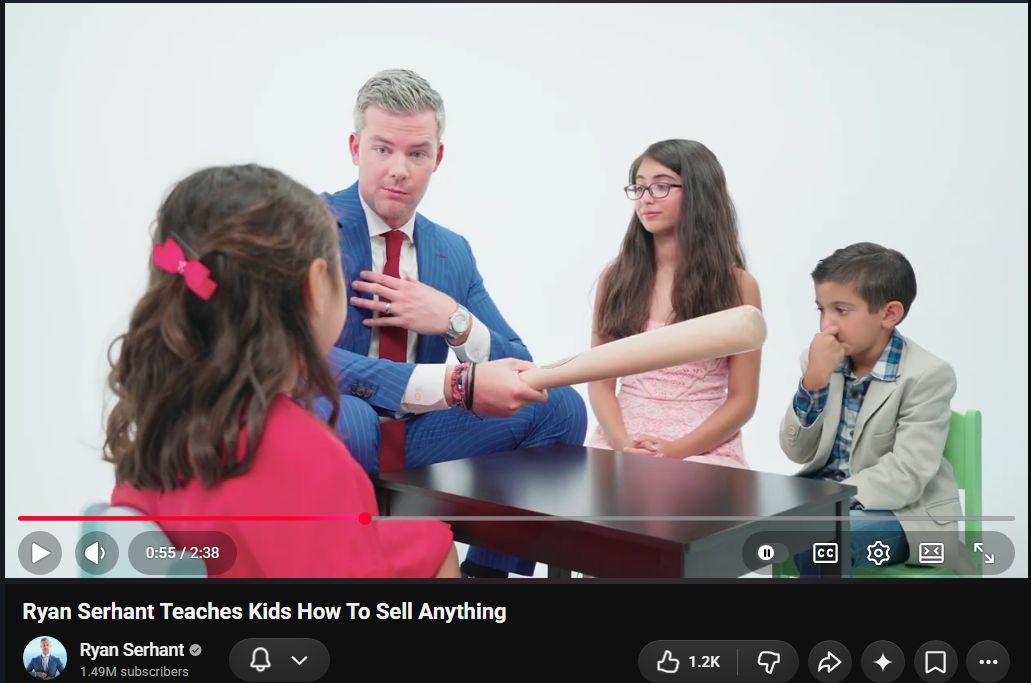
“… sell this to people who might hit people. What they do with that bat is not our responsibility.” Amercia in a f*cking nutshell…
PHP Exploit Quick-Fix for PHP2Shell
One idea for quick-fix. Not very tested. Use at your own risk. Patch up to latest PHP versions ASAP. …provided Apache has mod_security2 loaded and blocking is enabled. Use: SecRuleEngine On SecRequestBodyAccess On SecRule ARGS_NAMES “@rx (?i)^PHP_SESSION_UPLOAD_PROGRESS$” \ “id:10961801,phase:2,deny,status:403,log,msg:’PHP2Shell upload-progress blocked'” phase:2 lets ModSecurity parse the multipart body, then rejects it before Apache forwards the … Read more
The Grabsteria of Cloudflare et al
Think twice. Cloudflare’s “prove you are human” wall is not a neutral speed bump; it is an involuntary inspection booth wedged between readers and the web. Their own Turnstile privacy addendum says the system processes “client-side signals” including IP address, TLS fingerprint, User-Agent header, sitekey, and origin, and that the same addendum applies to Cloudflare’s … Read more
Good Riddance, Adobe
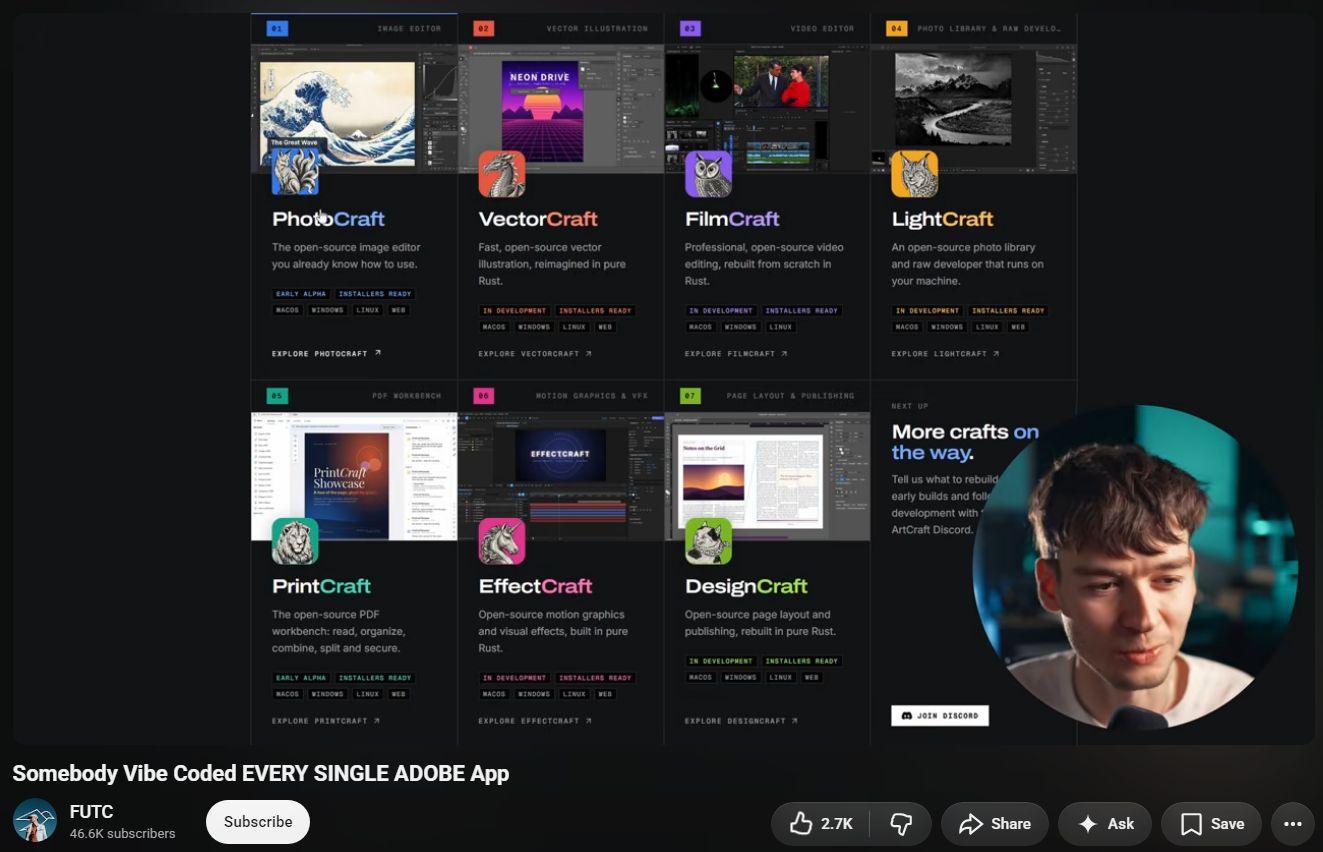
A great use of AI and open-source. Deeply, thoroughly open-sourced in fast, solid RUST language, https://github.com/storytold/photocraft is clean-room reimplementation — recreation of the workflows, muscle memory, panels, formats, and habits without copying Adobe’s proprietary code/assets. In other words: not “piracy,” but far more humiliating: A public dashing of its empire as mechanically reproducible. Adobe is … Read more
ChatGPT Halloween Hike – A Suddenly Quadrupled Price
Just received this email from OpenAI / ChatGPT: “Starting October 30, 2026, your included usage in ChatGPT Work and Codex will decrease from 20 times to 10 times the ChatGPT Plus allowance. Your GPT-6 Pro limit in Chat will decrease from 200 to 100 messages per week. Your price remains unchanged and you’ll keep your … Read more